And there will be a live stream as well:
https://www.youtube.com/live/4PNiwX4Go5A
We’re going to see this tonight … 🤩🎻
https://www.youtube.com/watch?v=R_3da0fPLQs
Walking
Still here for the craft. Don’t @ me. 😁
Feels like this is the final boss … 👾
Client’s sending half-baked prototypes again and asking if they can just add them to the site themselves.
Thanks, Dario!
Official #php2shell soundtrack just leaked:
And seeing all the reports from people waiting for their hosting providers to patch the servers their clients’ sites run on (myself included), and with all-inkl.com, the host I moved away from, still down, there’s also something to be said for taking care of some things yourself – and choosing your hosting provider carefully.
Still, hang in there, everyone patching things late into the night! 🫶
My first reaction to #php2shell was: “Dang, that’s the thing with running your own VPS – you have to keep everything up to date yourself…”
But: my own site is already running on #PHP 8.4.27. ✅
RE: https://fedi.katze.sh/@elise/117479383739450605
Happy #PHP Groundhog Day!
The issue affects PHP-FPM, mod_php, php-cgi, FrankenPHP and LiteSpeed. Update as soon as your distro or repo has the packages. On shared hosting, you might ask your host whether they’ve patched already. #CyberSecurity #infosec #php
If you can't update yet or a patch is not yet available for your distro / repo: Apply the temporary mitigations from the advisory. Set them in php.ini, then restart PHP:
```
session.upload_progress.enabled = 0
post_max_size = 32M
upload_max_filesize = 30M
```
They reduce the risk but don’t fix it.
What could an attacker do? Read everything your site can read (config files with database passwords and secret keys, the entire database), change your site (spam links, malicious JavaScript, hidden backdoors), and use your server to send spam or attack others. 🥳
Again, those security releases PHP just shipped are just … 🤯
Those two bugs let anyone run their own code on your server with a single crafted request: no login needed, and it happens before your CMS or framework even starts. And proof-of-concept exploits are already circulating … 🧵
Update your PHPs, everyone:
“PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35 fix two critical vulnerabilities that can allow unauthenticated remote code execution. All PHP users are strongly encouraged to update immediately.”
Brainstorming multi-lingual use of Artemis
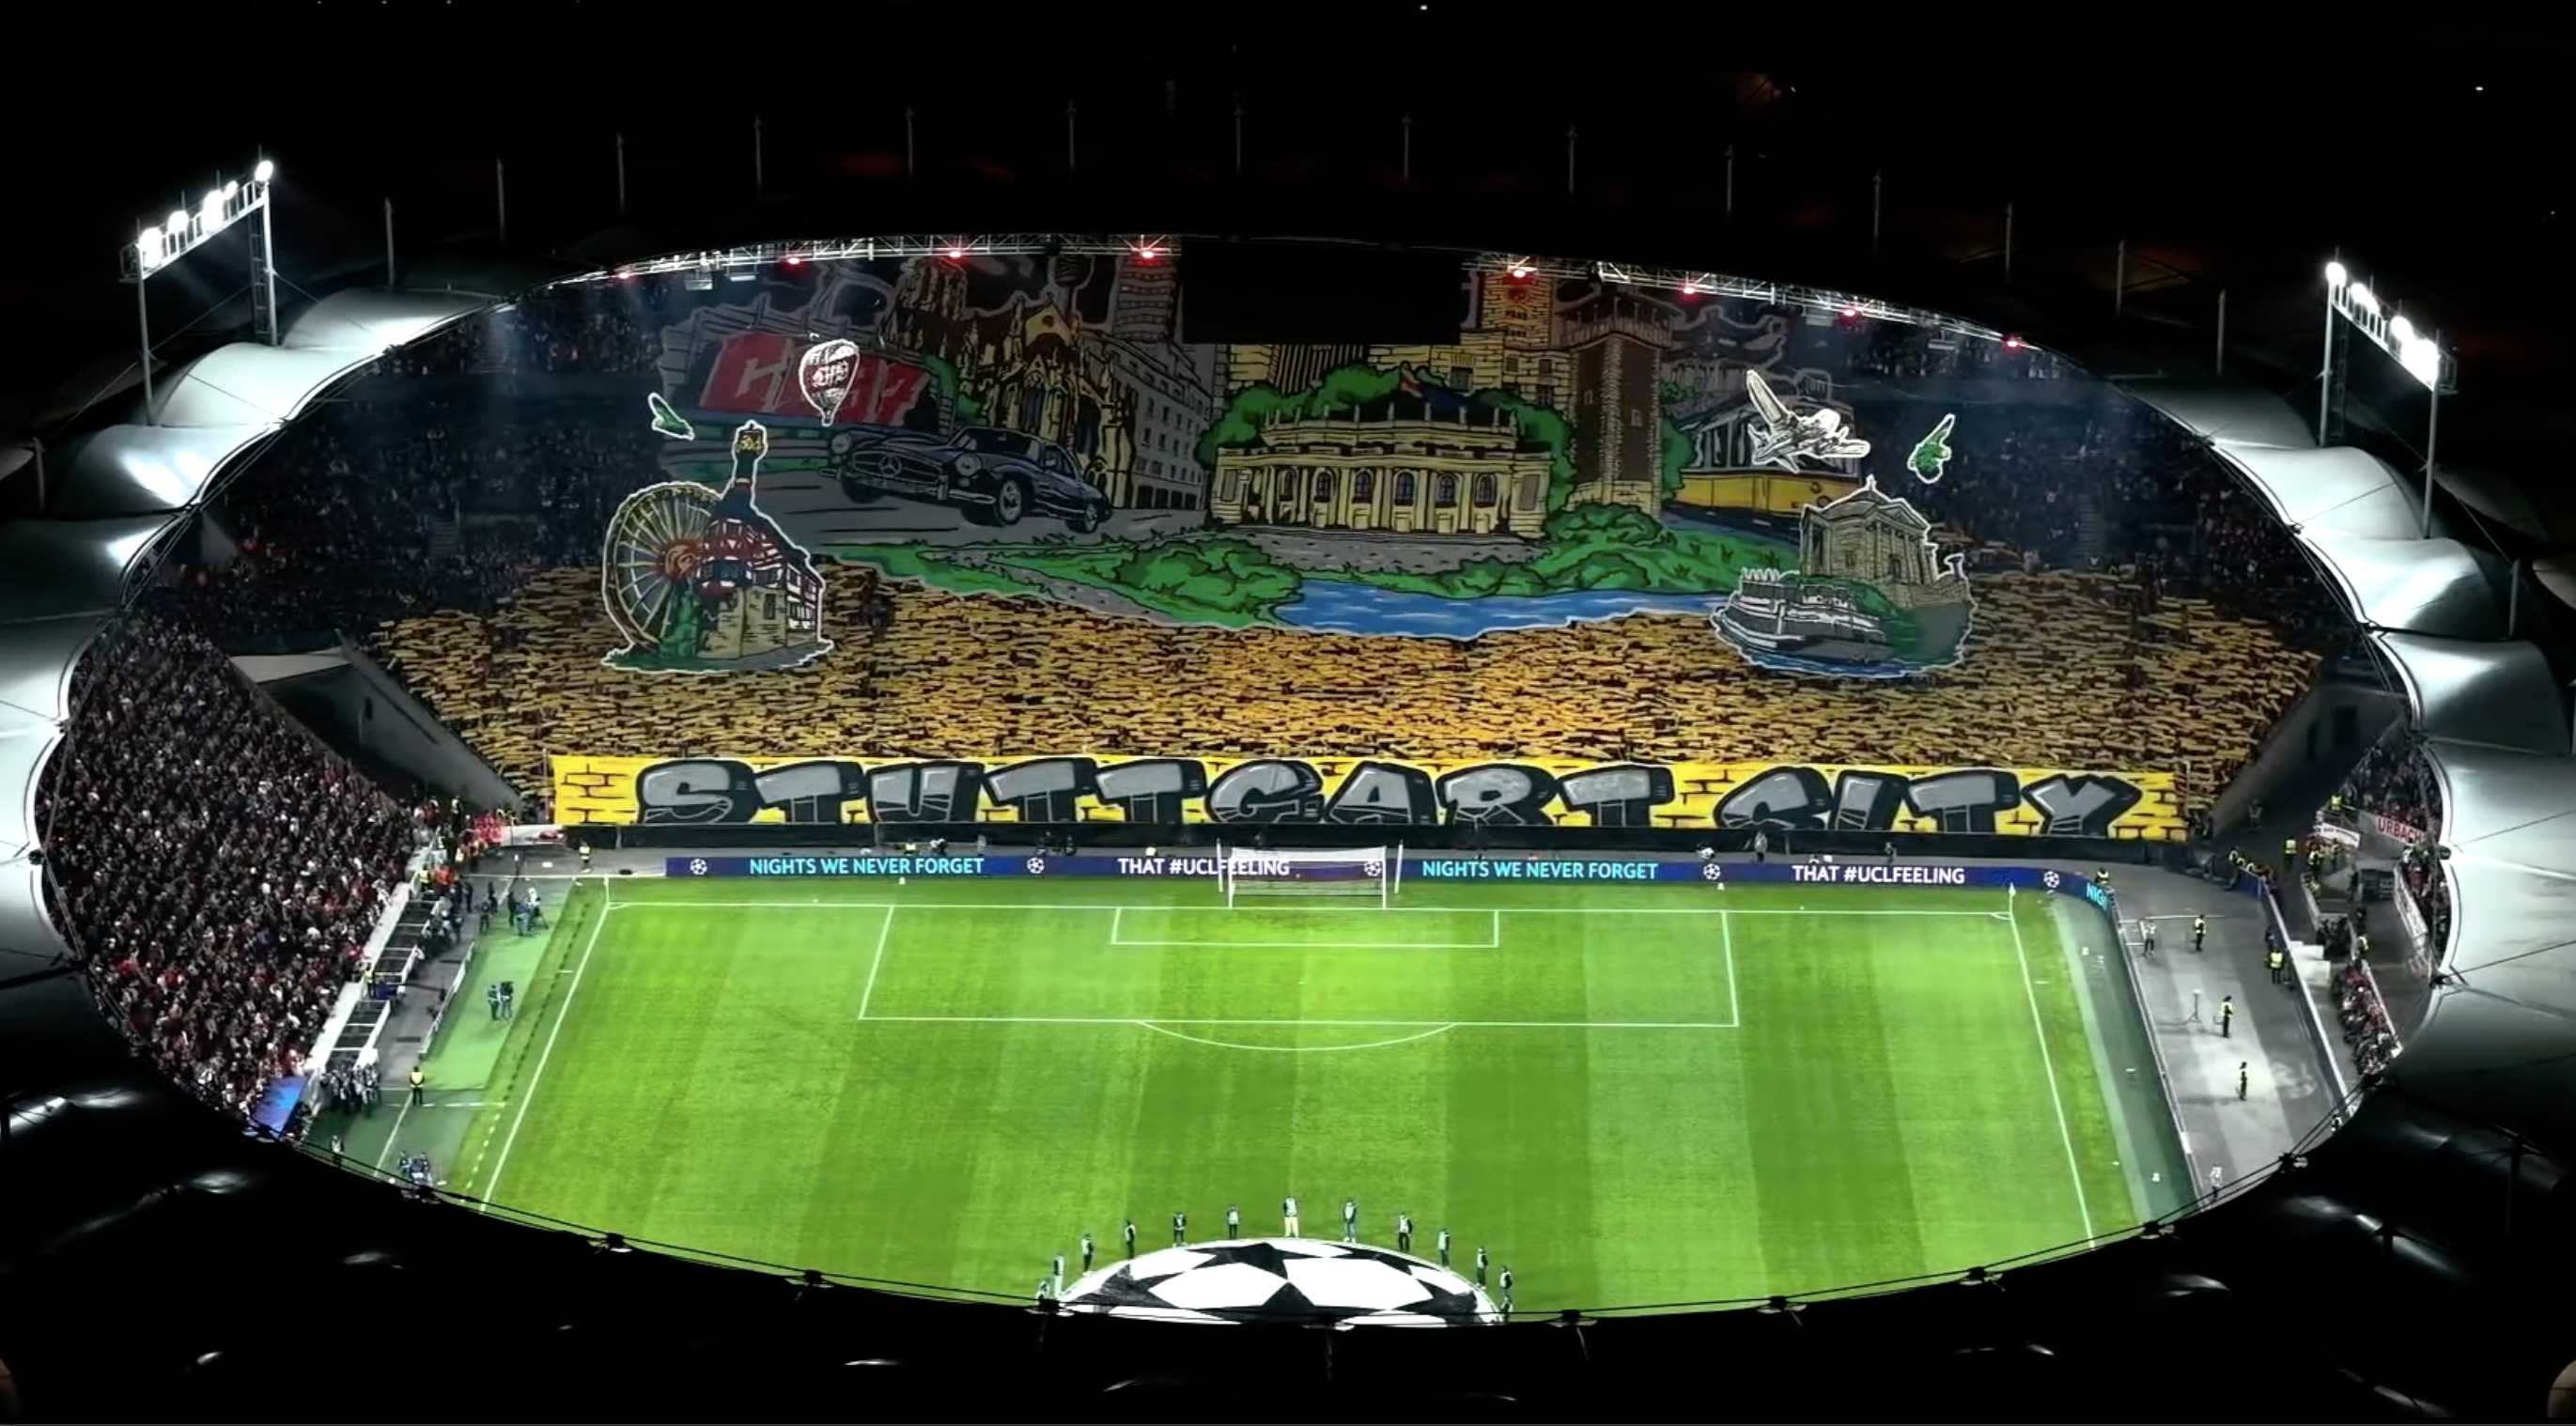
😍 #VfBATM
Queens of the Stone Age’s “Alive in the Catacombs” really is a recording for the ages. Literally.
(Also: 💀 Skull warning! Look up the Catacombs of Paris if you’re wondering about the setting …)